Built for teams where evidence is non-negotiable.
Three kinds of team we built for. The pattern under the names is the same: heavy audit work, real consequences for a miss, and tools that do not share data.
Life sciences & healthcare
For teams handling PHI and regulated product data: HIPAA, HITECH, 21 CFR Part 11/211/820, GAMP 5, ISO 27001 and the EU device rules, in one catalog.
Audits eat quarters. Vendor BAAs, validation evidence and the control set live in three different systems. Every customer security review starts with a search.
- ▸Catalog frameworks for HIPAA, HITECH, 21 CFR Part 11, 211 and 820, GAMP 5, IEC 62304, EU MDR and EU IVDR, ISO 27001 and ISO 9001
- ▸Agreements linked to the vendor record, with versions, reviews and AI obligation extraction
- ▸Validation evidence stored against the controls it supports
- ▸Inbound security questionnaires answered from your own control state
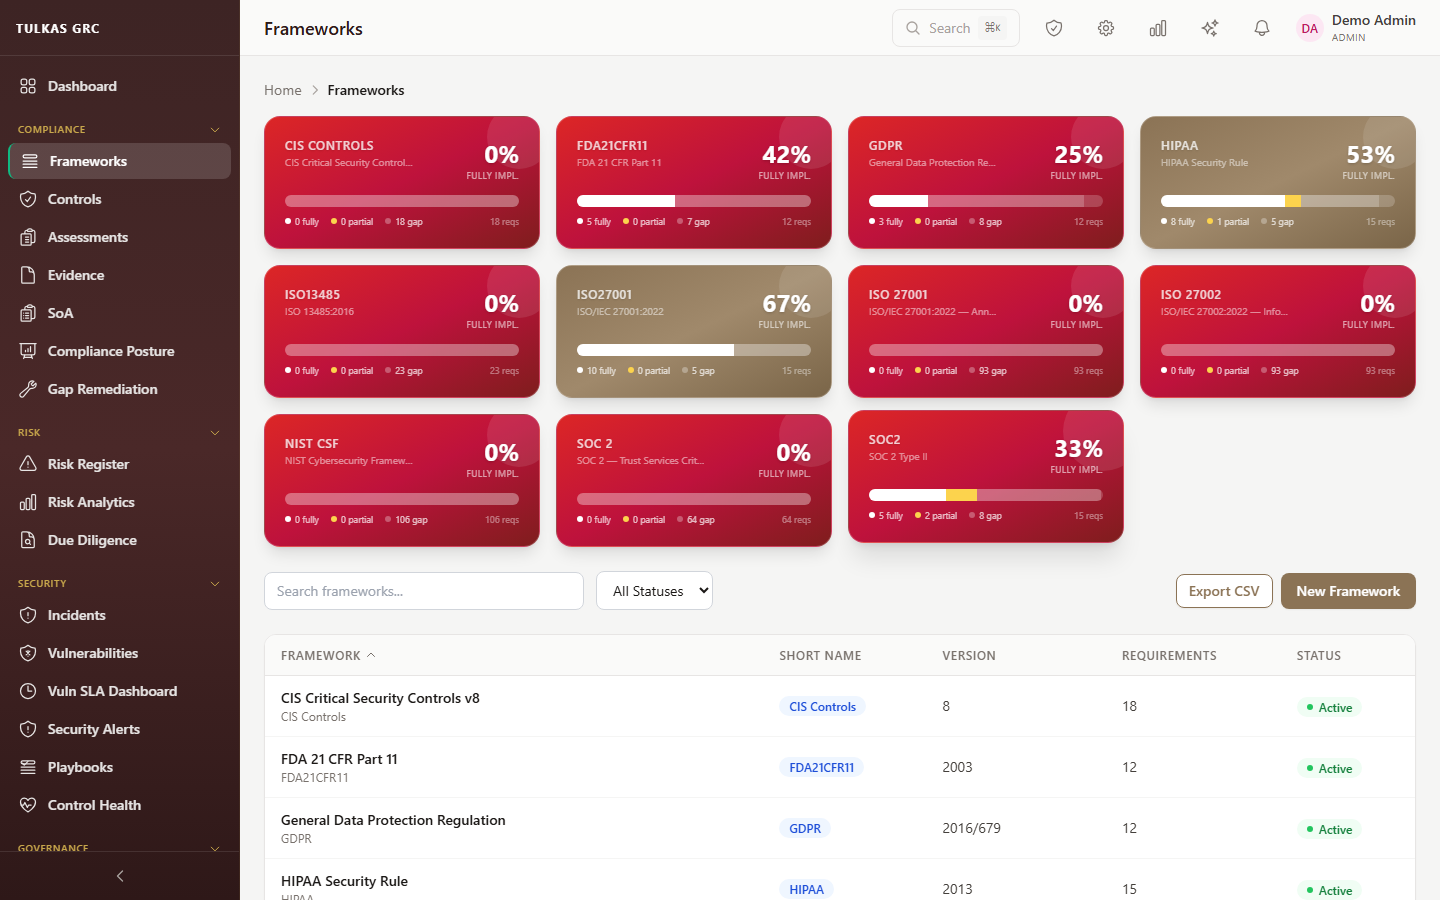
Multi-framework view. HIPAA, ISO 27001 and SOC 2 in one tenant.
B2B SaaS
SOC 2 and ISO 27001 for engineering-led teams, with exposure scanning and customer security reviews on the same data.
Compliance turns into a fire drill before each audit. Engineers dislike questionnaires. Scanner output lives somewhere the audit tool never sees.
- ▸Evidence from AWS (Config, Security Hub, GuardDuty, IAM access data), Microsoft Entra ID and Intune, and Jira
- ▸prowler for cloud posture, trivy for images and IaC, kube-bench for clusters, run from one scan plan
- ▸Findings mapped to the controls and framework requirements they affect
- ▸Vendor discovery from spend data and subprocessor tracking
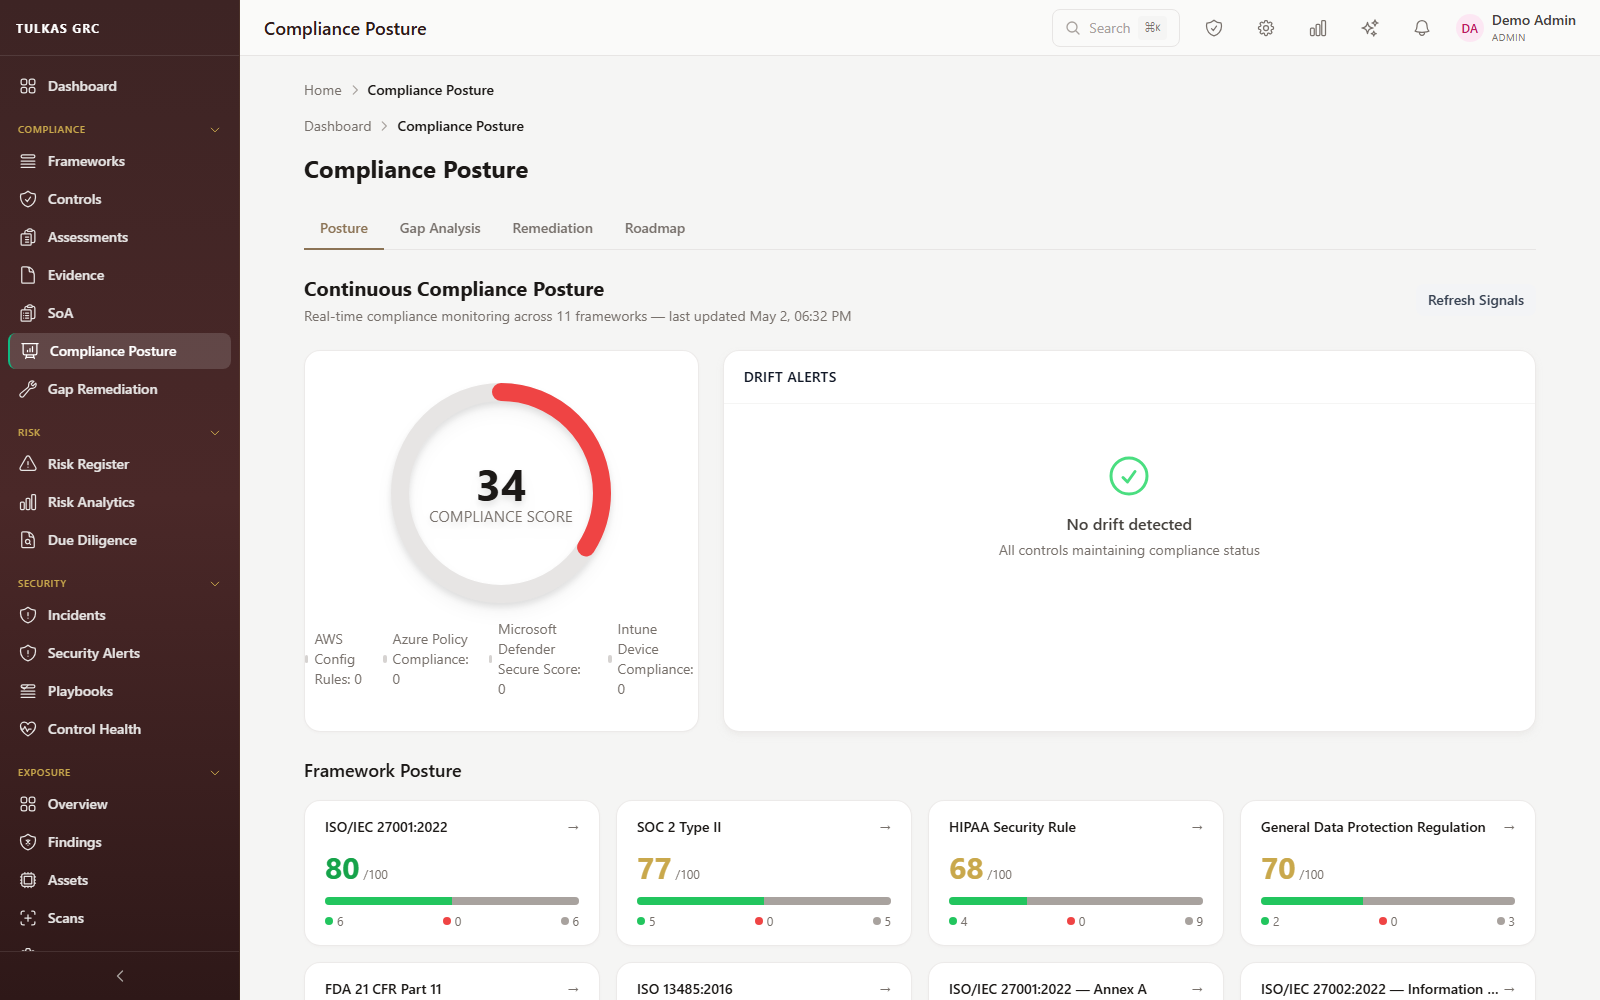
Compliance posture on a demo tenant.
Financial services
Audit trails that hold up to review, vendor records with the agreements behind them, and catalog frameworks for NYDFS 500, FFIEC, GLBA, SOX and DORA.
Exams need binders of evidence. Fourth-party risk is a guess. Contract obligations live in Word files nobody reopens after signing.
- ▸Catalog frameworks for NYDFS 500, FFIEC CAT, GLBA, SOX and DORA
- ▸Subprocessor tracking on each vendor record
- ▸Obligations extracted from agreements and kept on the contract record
- ▸Hash-chained audit events, so tampering with the trail is detectable
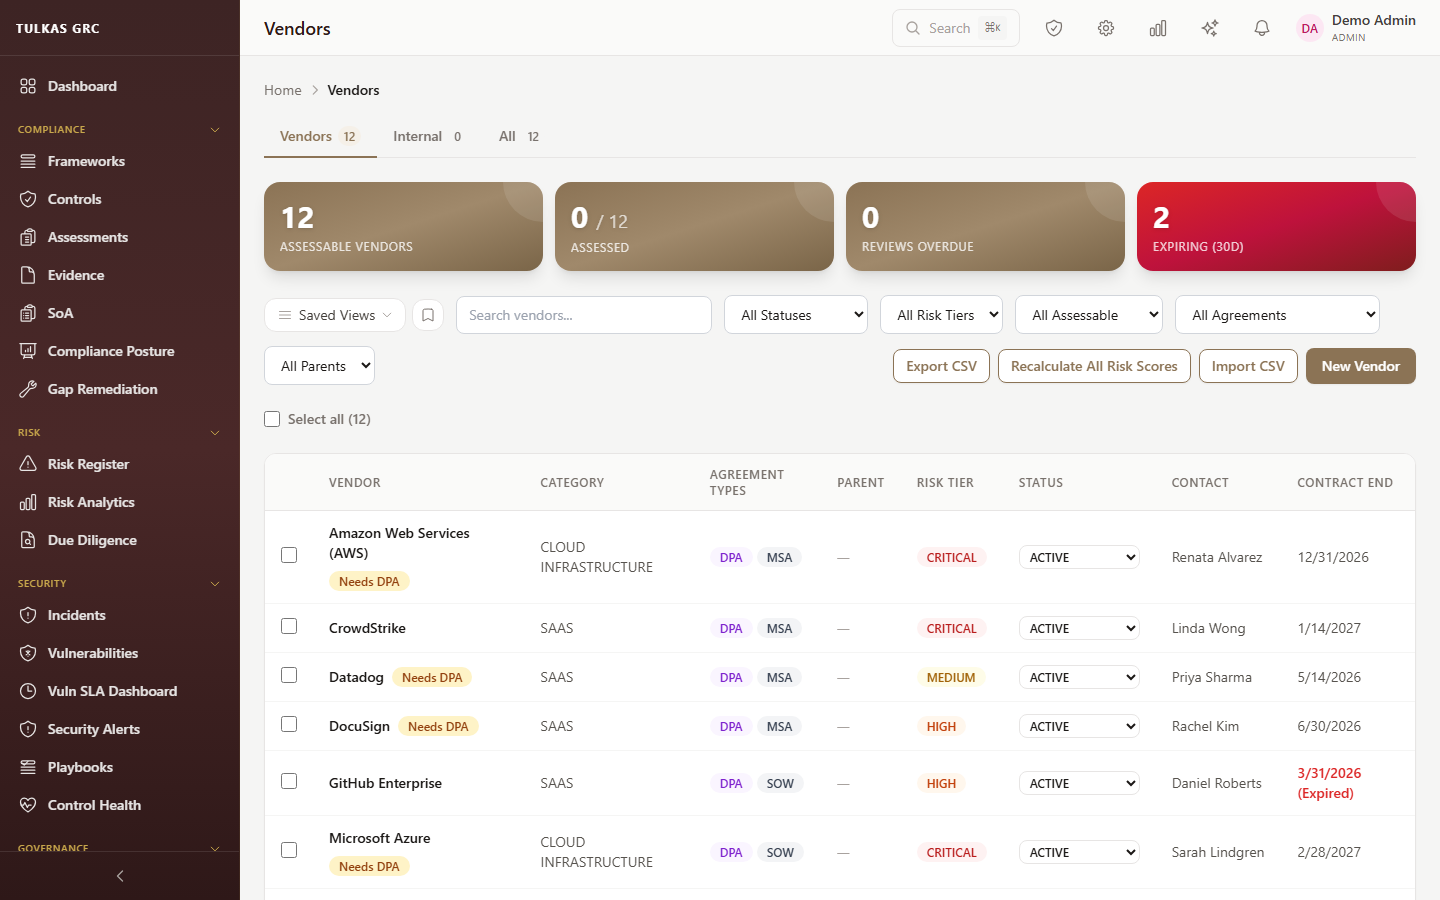
Vendor register on a demo tenant.
Industry not listed?
The platform is industry-agnostic; these three are where we started. Send us your context and we’ll tell you straight whether opsnite fits, and where it does not yet.