Automated Penetration Testing.
Scoped, automated pen test runs with a kill switch and a report.
Declare the scope, start the run, stop it whenever you want. opsnite drives the scan engines against your declared targets and writes up what it found as a PDF report. Findings land in the vulnerability queue with the controls they affect.
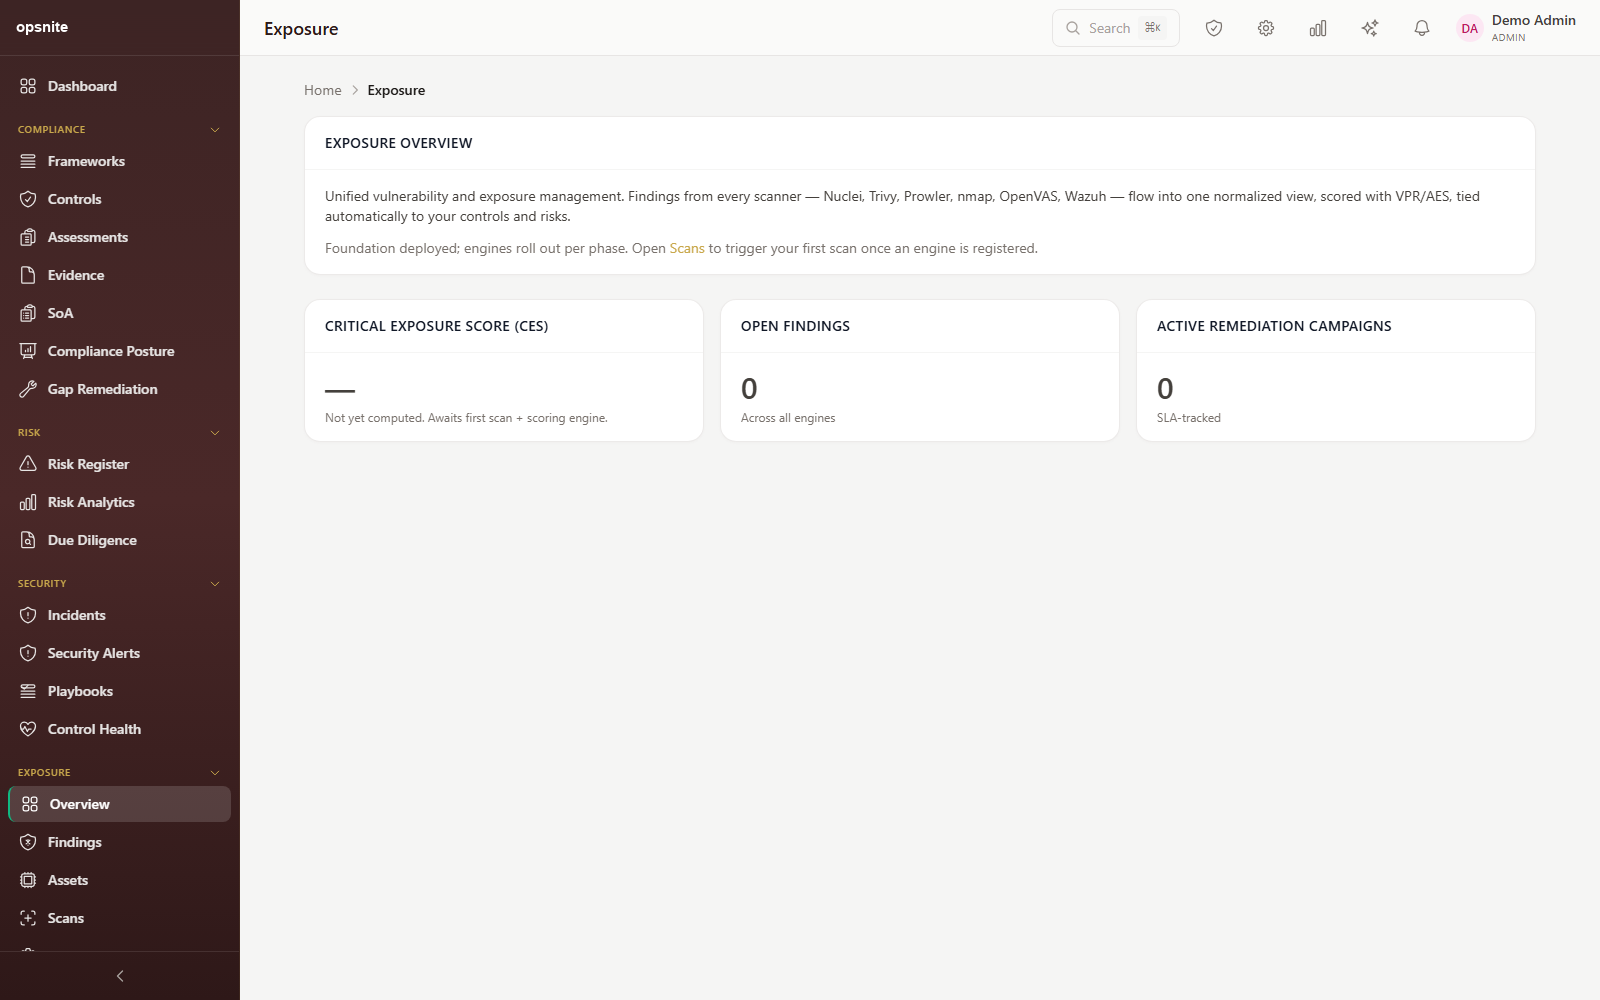
Exposure overview on a demo tenant, before its first scan.
What it does today.
Declared scope
Targets and rules are declared before a run starts, so what was in scope is on record when the auditor asks.
Kill switch
Every run has a kill switch. You decide when it stops.
Adversary mode
Adversary mode narrates how an attacker could chain findings across the risk graph, from an exposed asset to the requirement it puts at risk.
Where it stands
Built and tested in-house. It hasn’t been used on a customer engagement yet, and it doesn’t replace a third-party pen test when your auditor requires one.
What you get out of it.
- Scope on record before anything runs
- Findings flow into the same vulnerability queue
- Attack paths explained in plain language
- A report built from the data, not assembled in Word
Every name here is in the product. “(built)” means the connector switches on with your credentials but hasn’t run against a live customer system yet.
Stronger together.
Modules share one schema, so each one reads the others’ records. Three that pair naturally with this one.
See Pen Test with your own questions.
Send us what you need it to answer and we’ll walk you through the module on our demo tenant.