Contracts and Obligations.
Agreements, renewals and obligations, linked to vendors and risk.
Contracts live next to the vendors and processing activities they govern. Each agreement carries versions, reviews, approvals and milestones, and the AI pulls out the obligations (notice periods, audit rights, data residency, breach windows) so they reach the people who owe them. Signing stays in your e-signature tool; executed DocuSign envelopes import.
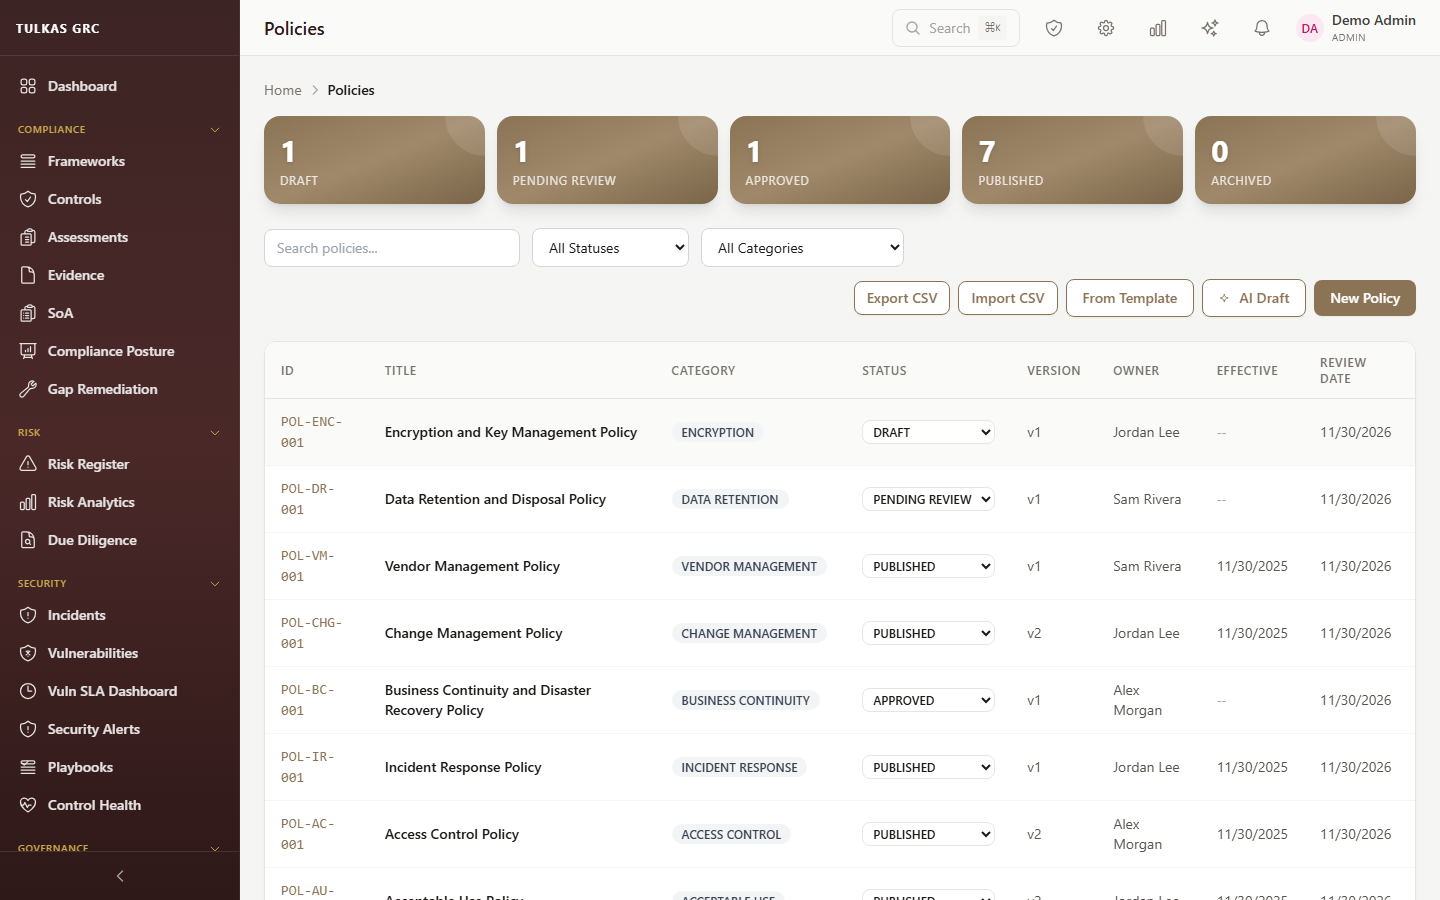
Document and policy library, demo tenant (sample data).
What it does today.
Agreements with history
Versions, reviews, approvals and milestones on every agreement, linked to the vendor and the processing activities it covers.
Obligation extraction
Notice periods, audit rights, data residency commitments and breach notification windows, extracted by the AI and assigned to an owner. Extraction is quota-limited per tenant.
Imports
Executed envelopes import from DocuSign. Existing contract libraries import from Cobblestone.
What it doesn’t do yet
No in-product signing, no Word redlining, no clause-library scoring. Those are on the roadmap, not in the product.
What you get out of it.
- Renewals and notice periods surface before they bite
- Contract obligations feed the control register
- Every agreement linked to the vendor it covers
- Plain scope: tracking and obligations, not a full CLM suite
Every name here is in the product. “(built)” means the connector switches on with your credentials but hasn’t run against a live customer system yet.
Stronger together.
Modules share one schema, so each one reads the others’ records. Three that pair naturally with this one.
See Contracts with your own questions.
Send us what you need it to answer and we’ll walk you through the module on our demo tenant.