Vendor Risk Management.
Vendors, questionnaires, documents and subprocessors, tied to your controls.
Third-party risk for teams that buy a lot of SaaS. A vendor register with assessments, questionnaires and approvals, documents with expiry dates, and subprocessor tracking, all linked to the controls and contracts they affect. Spend data finds the vendors nobody registered.
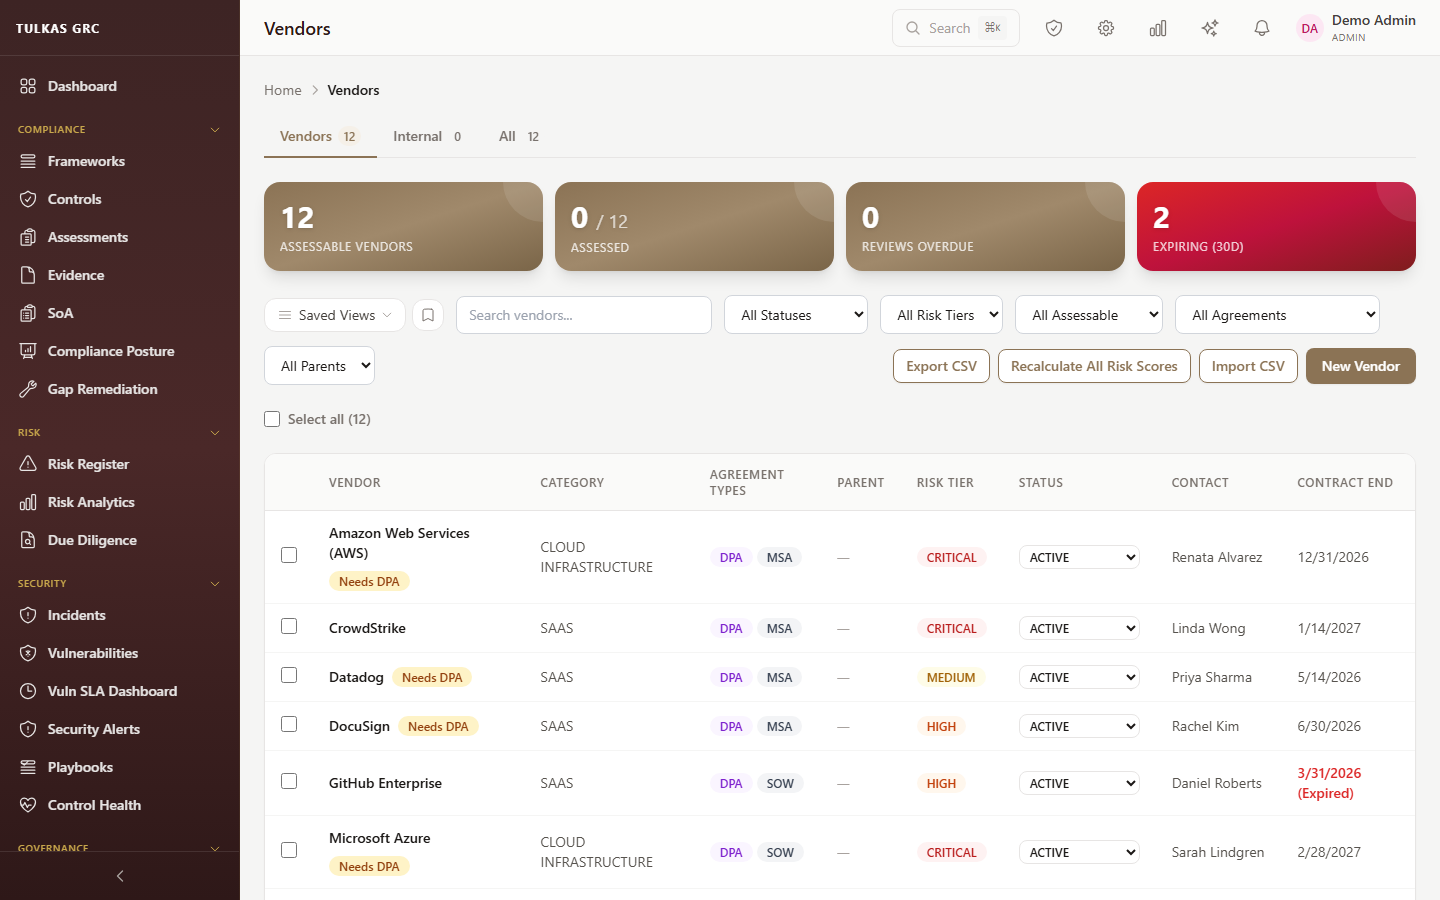
Vendor register, demo tenant (sample data).
What it does today.
Register and approvals
Vendors land in one register with assessments, approvals and risk snapshots over time, linked to controls, contracts and processing activities.
Questionnaires in both directions
Send questionnaires to vendors and track the responses. Answer inbound security questionnaires from your own control data instead of from memory.
Documents and expiry
DPAs, SOC 2 reports and other vendor documents live on the vendor record with their expiry dates.
Vendor discovery from spend
Point it at expense and spend data and it surfaces vendors that never went through intake. Subprocessor tracking shows who your vendors depend on.
What you get out of it.
- Shadow vendors found in spend data, not on a surprise invoice
- Vendor documents and expiry dates on one record
- Inbound security questionnaires answered from control data
- Vendor risk linked to the controls it affects
Every name here is in the product. “(built)” means the connector switches on with your credentials but hasn’t run against a live customer system yet.
Stronger together.
Modules share one schema, so each one reads the others’ records. Three that pair naturally with this one.
See Vendor Risk with your own questions.
Send us what you need it to answer and we’ll walk you through the module on our demo tenant.